 Inspect image
01SOC Analyst / Security Investigator
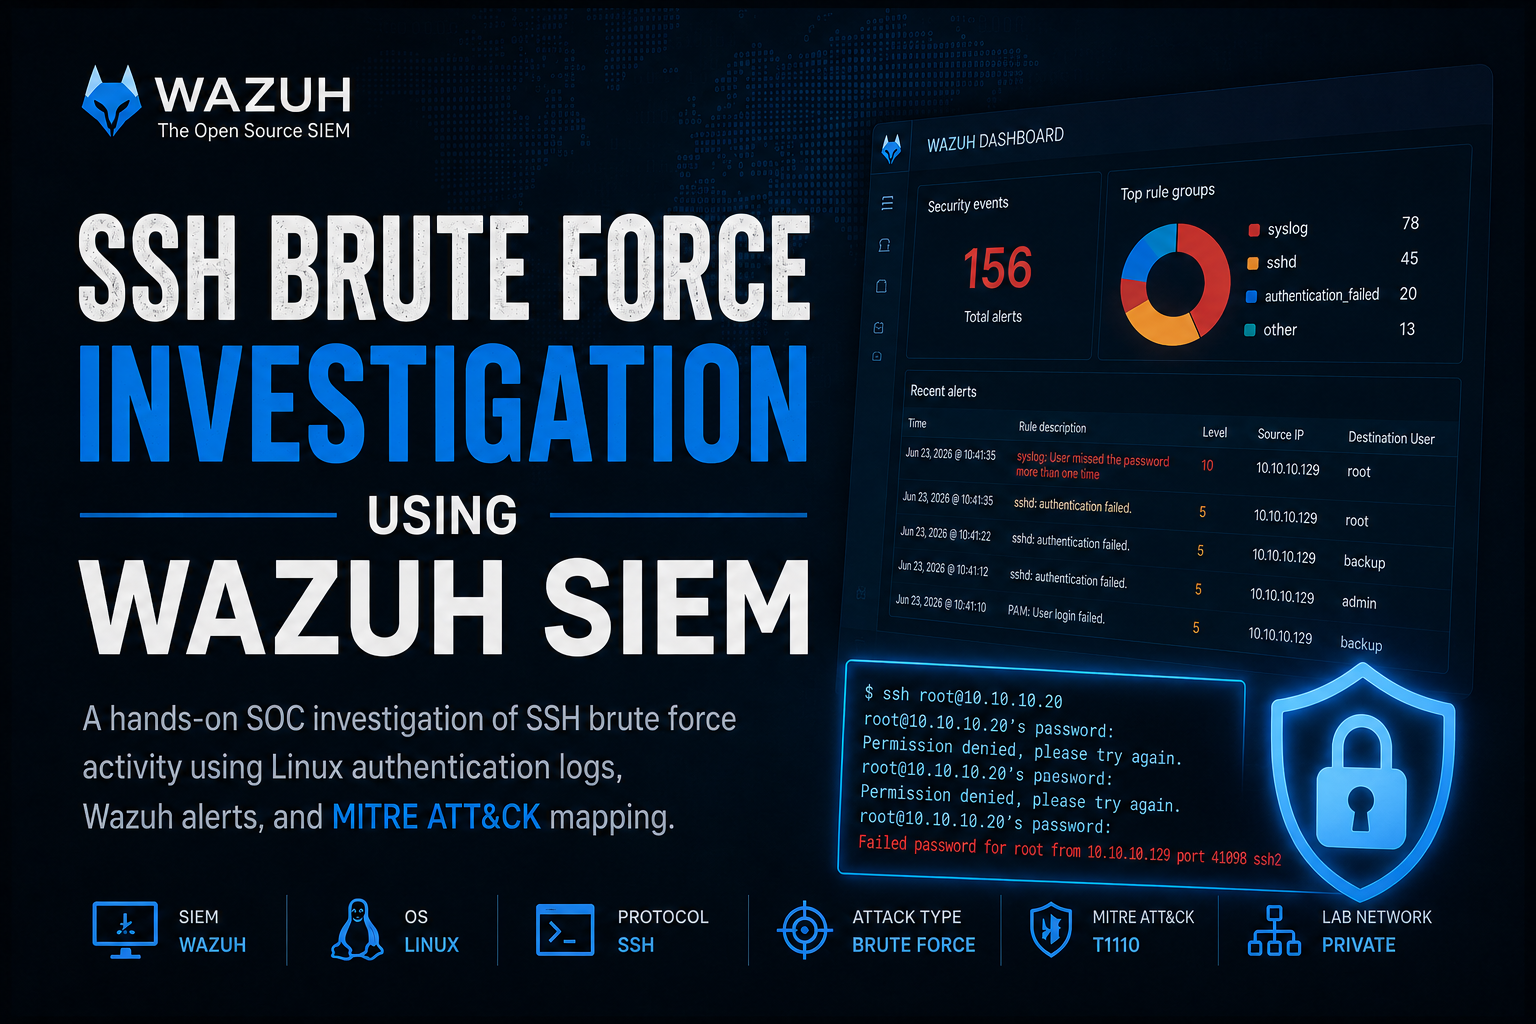
SSH Brute Force Investigation using Wazuh SIEM
Built a hands-on Wazuh SIEM investigation lab to detect and analyze SSH brute-force activity using Linux authentication logs and endpoint telemetry. Correlated failed SSH login attempts with Wazuh alerts to identify the attacker source IP, targeted accounts, MITRE ATT&CK T1110/T1110.001 mapping, and confirmed that no successful authentication occurred.